CrowdStrike and CoreWeave Partner to Deploy AI Security at Machine Speed
As cyberattackers breach networks in seconds, CrowdStrike and CoreWeave are combining security expertise with specialized computing infrastructure to build defenses that operate faster than human response times.
Protecting AI systems from modern threats demands security measures that can match the velocity of attackers while maintaining continuous operation of infrastructure that trains and runs models. This convergence is pushing security capabilities and high-performance computing into closer alignment, with automated defenses woven throughout enterprise machine-learning pipelines.
In 2025, CrowdStrike Holdings Inc. documented an eCrime attacker achieving full system compromise in just 27 seconds, illustrating the critical need for accelerated detection and response. Bartley Richardson, chief of AI at CrowdStrike, emphasized that meeting this threat requires both training and inference computing resources. "You can't have humans combat this alone," Richardson said. "You need machine-speed defense, and that relies on critical infrastructure."
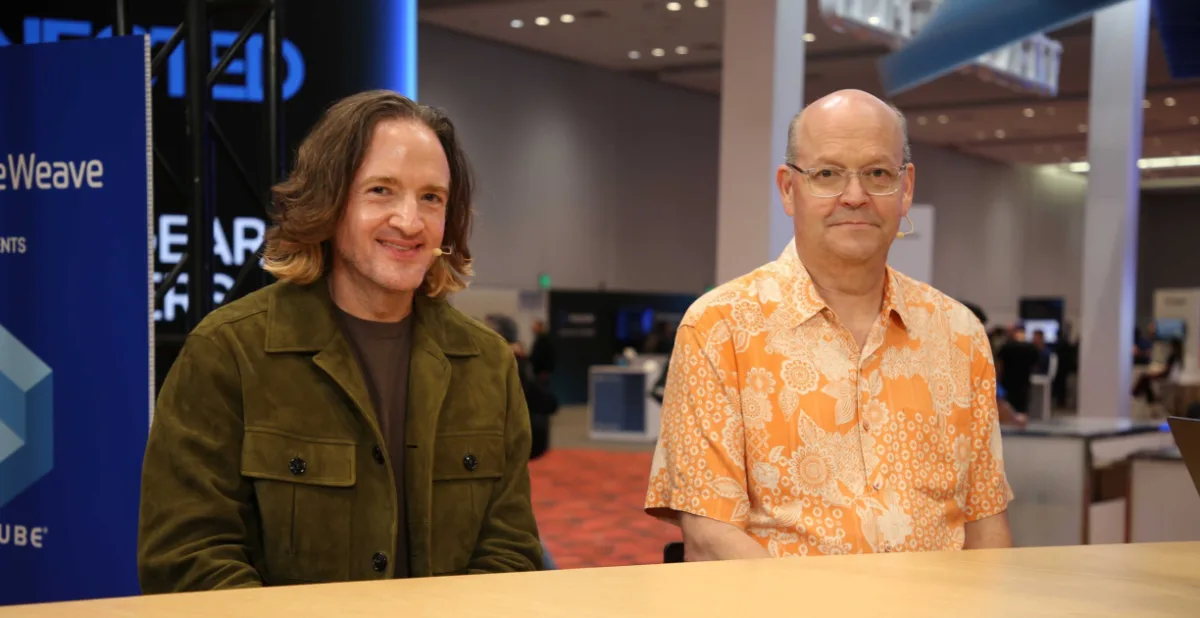
Richardson and Jim Higgins, chief information security officer of CoreWeave Inc., discussed the partnership during an exclusive broadcast at the Fully Connected event, hosted on theCUBE, SiliconANGLE Media's livestreaming platform. Their conversation with theCUBE Research's Dave Vellante and John Furrier covered machine-speed defense, infrastructure-level security and operational trust.
Cyber models turn attacks into training data
The collaboration merges CrowdStrike's security intelligence and threat knowledge with CoreWeave's computational infrastructure. CoreWeave provides both training and inference resources for SafeMind and functions as a design partner for CrowdStrike's Cyber Superintelligence Lab.
Richardson described the strategic approach: "The name of the game … is adversarial co-evolution, which is a fancy way of saying, 'We train and we steer the best offensive capabilities to attack, to find ways around defensive operations.' But then, we train these defensive models on large-scale infrastructure to learn from those attacks."
CoreWeave faces the challenge of strengthening defenses without interrupting its production systems. Higgins explained that this requires embedding security measures into live operations rather than halting them. "That's what I refer to as the aikido of the security problem," Higgins said. "Anything that I can do to affect security while the machine is running and use its own energy to promote the security needs is exactly what I do. Using AI to support and scan my code is incredibly important, but also to be in the [continuous integration and continuous delivery] pipeline to use automation to fix misconfigurations."
AI-native cybersecurity still starts with the basics
Attackers operate under resource and time constraints, making straightforward entry points their preferred targets. Higgins noted that combining multiple common vulnerabilities can create the access they need. "When you say something is secure, test it and test it often to be sure, but also do the basics," Higgins said. "Patch your stuff and continually test and monitor for those issues."
https://www.youtube.com/embed/Pdltp8QUcXA?feature=oembed
CrowdStrike is channeling resources into automation for round-the-clock security monitoring. These systems must gain the trust of CoreWeave and its customers before they can be fully relied upon, according to Richardson. "People ask, 'When do we get to the end of AI?' And I say, 'Never,'" Richardson said. "And then I tell them, 'It's because it's AI until you trust it. Then you start to think of it as automation.' As we make our investment into AI that's always on, what's so important for us is how trust is built into the system."